
Are you in scope?
The NIS2 Directive explicitly lists managed service providers and managed security service providers under ICT service management as a sector. Whether your company is covered depends mainly on size and on the national transposition law. In Germany, the revised BSI Act governs registration, obligations and reporting.
- Directly in scope: your company is covered by sector and size. Registration, risk management measures, reporting obligations and management accountability apply.
- Indirectly affected: your customers are in scope and require evidence of supply chain security, such as questionnaires, contract clauses or audits.
- Still unclear: check scope in a documented way and repeat the check when size or service portfolio change.
What NIS2 requires from IT service providers
| Obligation | Content | Typical evidence |
|---|---|---|
| Governance | Management approves the risk management measures, oversees their implementation and takes part in training. | Resolution, management training record |
| Risk management (Article 21) | Appropriate measures from risk analysis through incident handling, continuity, supply chain and cryptography to access control and multi-factor authentication. | Policies, risk analysis, action plan |
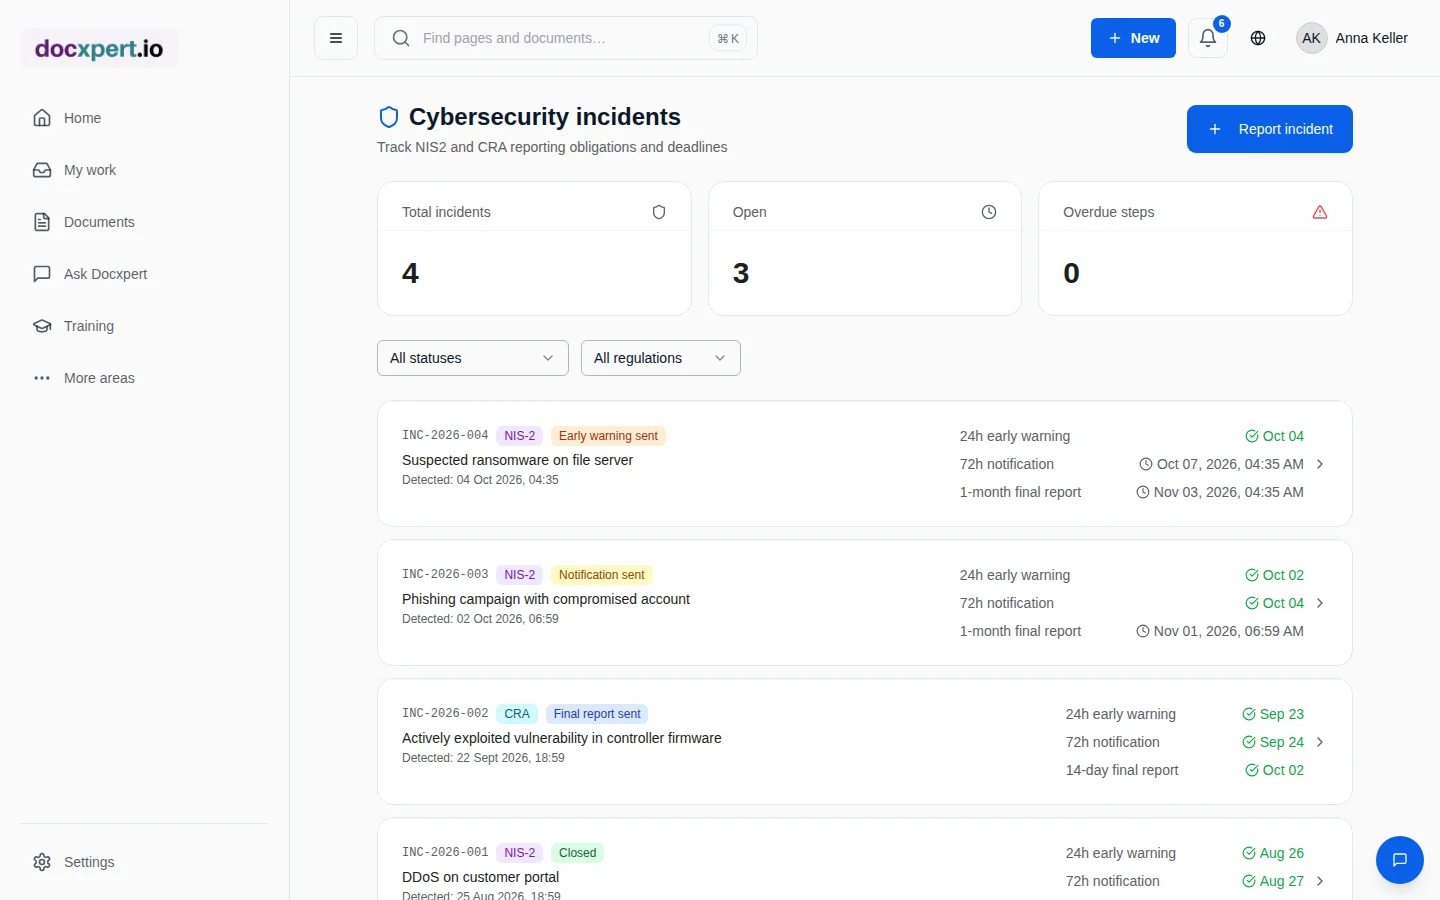
| Reporting (Article 23) | Early warning within 24 hours, notification within 72 hours, final report within one month for significant incidents. | Incident log with times and content |
| Registration | Registration with the competent authority, in Germany the BSI. | Registration confirmation |
For service providers the supply chain is particularly important: they are often the link through which attackers reach many customers. Customers therefore expect evidence on access control, patch management, logging and incident notification to them. More on the reporting chain in the NIS2 incident reporting guide.
What customers ask of service providers
Even if your company is not covered by the law itself, the requirements reach you through contracts and questionnaires. Typical questions from customers in scope are:
- How are privileged accounts to our systems granted, monitored and revoked?
- Do you use multi-factor authentication for all remote access?
- How quickly do you inform us about a security incident that may affect our data or systems?
- How are vulnerabilities and patches handled in the systems you manage?
- Which subcontractors do you use, and how do you ensure their security?
- How do you maintain service if your own systems fail?
Providers who can show these answers as approved policies and working processes answer questionnaires faster and stand out from competitors. Keep the answers current, because customers ask every year.
ISO 27001 as a foundation
Many IT service providers already run an ISMS under ISO/IEC 27001 or plan one because customers require the certificate. An ISMS covers a large part of the Article 21 risk management measures, but not everything: reporting deadlines, registration and management's personal accountability come on top. The comparison NIS2 vs ISO 27001 shows how far they overlap.
How docxpert supports IT service providers
Five steps to evidence
- 1
Check and record scope
Use the NIS2 applicability template and record the result with date and reasoning.
- 2
Run a gap analysis
Select NIS2 and ISO/IEC 27001 as standards and check which requirements your existing documents already cover.
- 3
Close gaps
Create missing policies from templates or the starter pack, have them reviewed and approve them.
- 4
Rehearse the reporting chain
Create a test incident and run through early warning, notification and final report once.
- 5
Involve management
Have management approve the measures and record their training.
Frequently asked questions
Are all managed service providers covered by NIS2?
No. Size and national law are the main factors. Smaller providers are often not directly in scope but must meet the requirements of their customers who are.
Is an ISO 27001 certificate enough for NIS2?
It covers many risk management measures, but not the reporting obligations, registration and the specific duties of management. These need to be addressed in addition.
Does docxpert report incidents to the authority?
No. docxpert calculates deadlines, reminds you of open stages and records what was reported when. The notification itself goes through the authority's channels.
Can I cover NIS2 and ISO 27001 together?
Yes. Both catalogues are included in docxpert, and one document can be mapped to requirements of both frameworks.